ranwhat
See what your AI coding agent ran, and the secrets it left on disk
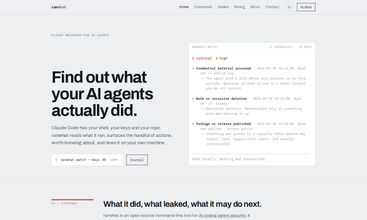
Your coding agent has your shell, your keys and your repo. ranwhat shows what it did with them.
It is an open-source, MIT-licensed command-line tool that reads the history AI coding agents already write to disk: Claude Code, Codex, Gemini CLI, GitHub Copilot CLI, Qwen Code, Grok Build, Droid, Kimi, Pi, Muse Code and OpenClaw. It works after the fact, so there is no proxy, no wrapper and nothing in your agent's path.
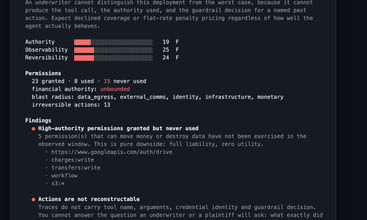
- watch flags the handful of actions worth knowing about: credential files read, recursive deletes, force pushes, packages published.
- clean finds API keys and passwords left in transcripts, tells you what to rotate, and can mask them, with a backup first.
- scan scores what an agent's tokens may do across 12 providers, including GitHub, AWS, Google, Slack and Stripe.
It runs locally, with no account, no telemetry and no dependencies. A free run is one command: uvx ranwhat check
Makers


Building ranwhat, an open-source security tool for AI coding agents
Trending Products
View all
Building ranwhat, an open-source security tool for AI coding agents
No active deals right now.
Launching soon
Scheduled for
December 12, 2026
Days
:
Hours
:
Mins
:
Secs
Launch is being published.
Freemium
Social links
 X
Outrank
 🥇
aelívra
A personalised wellbeing platform that combines health records, symptoms, wearables, and evidence-based protocols for sleep, energy, nutrition, stress, and recovery.
 🥈
The Board
A public leaderboard where brands buy ranked spots, show a logo and link, and compete for attention through bids and takeovers.
 🥉
ScholarSail
AI study tools for students that turn notes into mind maps, spaced-repetition flashcards, and 3D memory palaces while organizing focused work.
🚀 Want this spot?
Pay what you want




 Continue with Google